CuCM Secure Communication


CuCM Secure Communication |
|
| Standard > Use cases > Basic use cases samples |
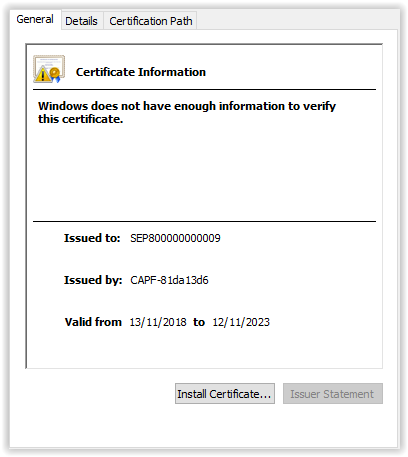
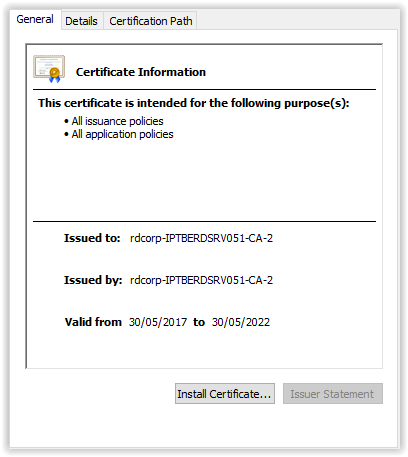
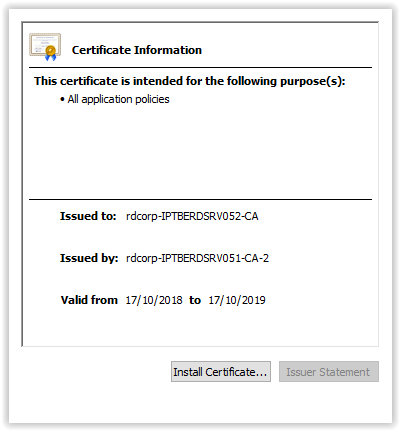
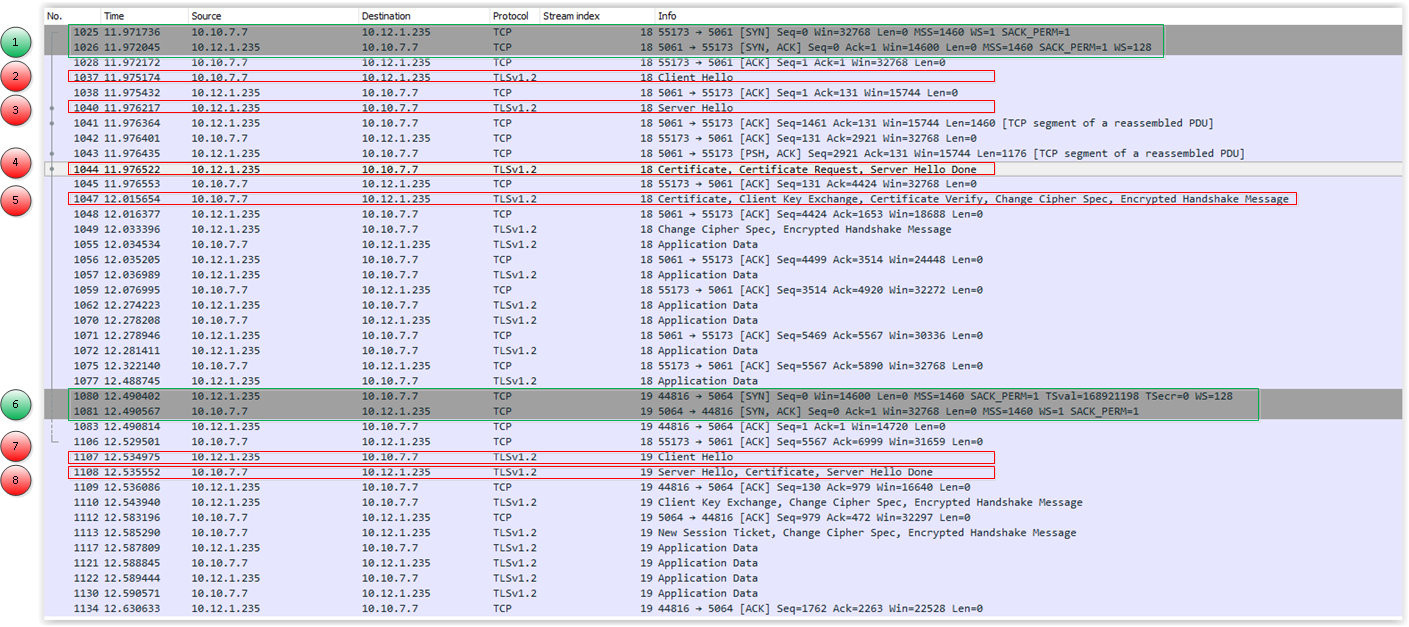
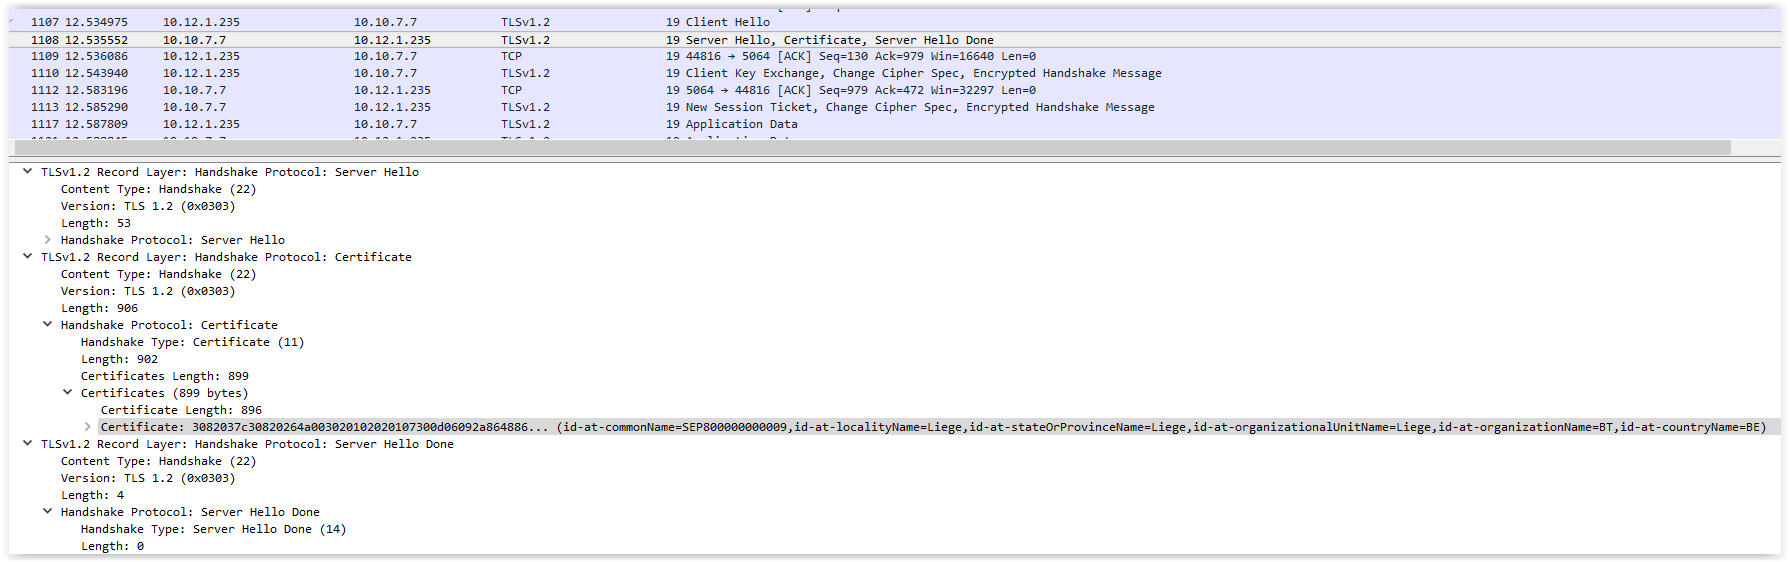
CuCM SIPS protocol uses mutual certificate authentication. It means the SIP endpoint (Device) must also provide a client certificate for a strong authentication. TLS connection between TPO and CuCM for SIP registrationContext•TPO: 10.10.7.7 •CuCM: cucm12pub.iptrade.local, 10.12.1.235 •Certificates: ➢Client certificate signed by CuCM CAPF Service ➢CuCM CAPF Certificate is signed by subordinate CA IPTBERDSRV052 ➢CuCM CallManager Certificate is signed by subordinate CA IPTBERDSRV052 ➢Subordinate CA Certificate is signed by CA IPTBERDSRV051 ➢CA Certificate is a self-signed •SIP Device Id used on TPO DDI place: SEP800000000009 •Extension: 8900 •Client Certificate: SEP800000000009.cer
•CA certificate:
• Subordinate CA:
ScenarioStart the TPO DDI place Result: place is started and Device SEP800000000009 is registered properly Network TraceWireshark filter: tcp.port == 5061 || tcp.port == 5062 || tcp.port == 5063 || tcp.port == 5064 || tcp.port == 5060 |