Remotely Capture Packets


Remotely Capture Packets |
|
| Basic > Troubleshooting Data: How to retrieve them > Turret > Wireshark Capture |
This topic contains procedure which allows taking traces on 3 Turrets at once.
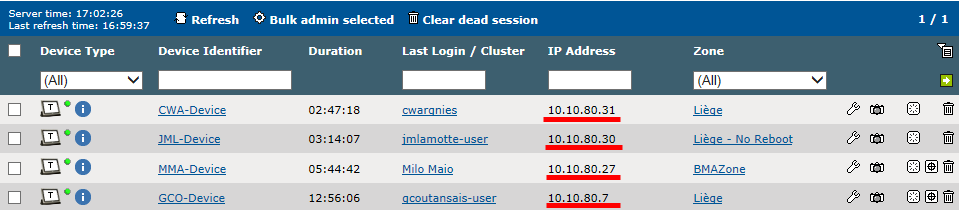
1.Ensure latest version of Wireshark is installed on your computer. 2.Get IP addresses of up to 3 involved Turret on which remote capture service has been started: a.Connect to the TSS administration console using an administrator account b.Navigate to System > Sessions > Device Sessions and apply relevant filter
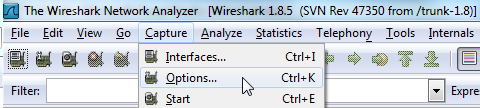
3.Launch Wireshark.exe 4.Navigate to Capture > Options
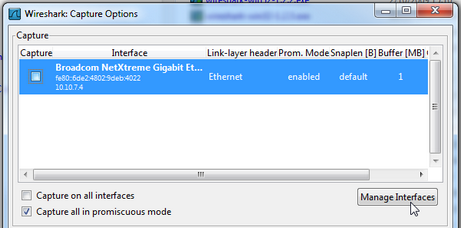
5.Click Manage Interfaces button
6.Select Remote Interfaces tab and click Add button
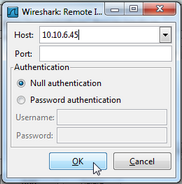
7.Type in one of the turret IP Address in Host field, leave Port field empty and Null Authentication selected.
8.Click OK button: Corresponding turret interfaces are listed
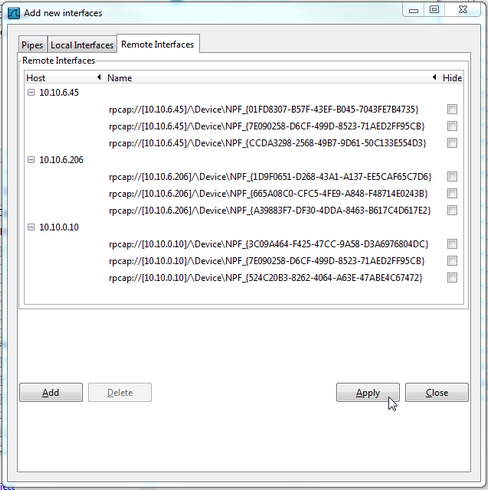
9.Repeat steps 6 to 8 for other turret IP addresses
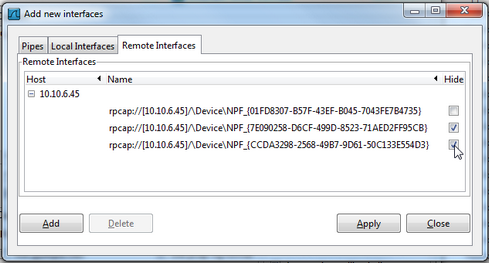
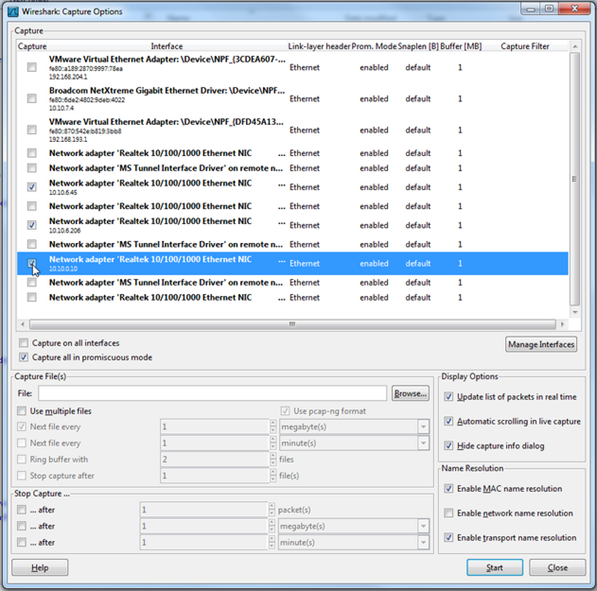
10.Uncheck Hide boxes for all interfaces 11.Click Apply button, and then, Close button 12.Uncheck Capture boxes of local interfaces and check Capture boxes next to the relevant remote interfaces (which are indicated by IP Addresses)
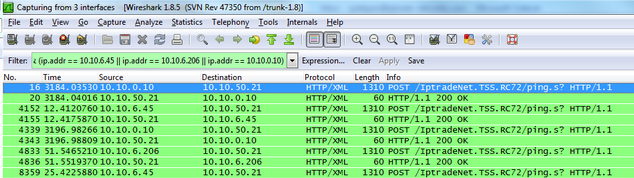
13.Click Start button in order to begin packet capture. You may apply a display filter based on interesting IP Addresses.
14.Wireshark shows "Capturing from 3 interfaces" and we can see corresponding packets in list
|